Infrastructure as Product
Your infrastructure. Your account. Our engineering.
A complete AWS stack, ready for production. No building from scratch, no depending on platforms that hide the infrastructure from you.
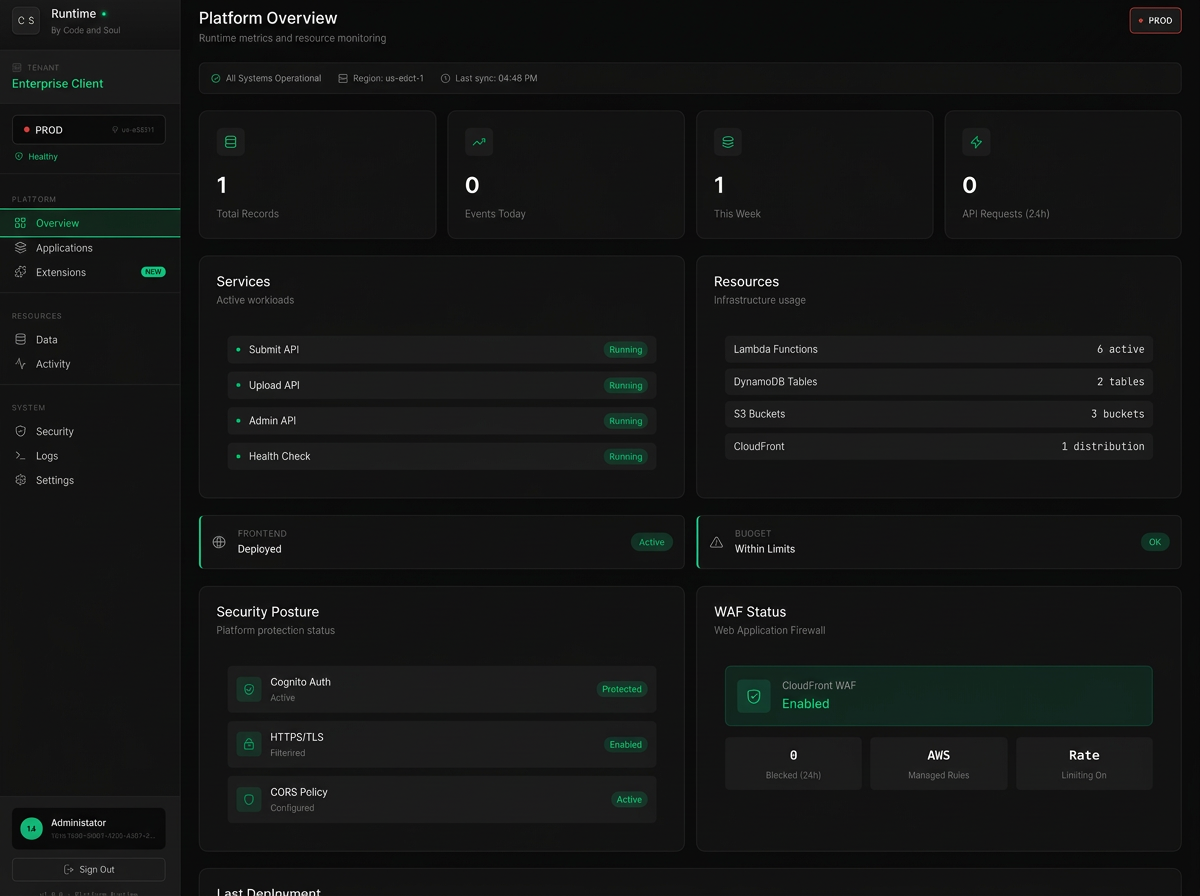
CloudFront, API Gateway, WAF, Lambda, DynamoDB, CI/CD with security gate. All in your AWS account, under your full control.
Why it exists
Three paths, none ideal
Most companies face the same dilemma when they need real cloud infrastructure.
Shared hosting has limits
It works until the day you need a global CDN, WAF, automatic rollback, or real control over the environment. Then there's no way out without starting over.
Generic PaaS creates lock-in
Vercel, Render, and similar solve deployment but hide the infrastructure. You don't control costs, can't configure security, and have no portability.
Building from scratch is expensive
Setting up an AWS stack with CI/CD, WAF, observability, and governance takes months and requires a dedicated senior team. Few companies can justify that investment.
What you get
Complete infrastructure, ready to operate
Every component is configured, tested, and delivered working in your AWS account. No surprises, no manual setup.
CloudFront CDN
Global distribution with intelligent caching, automatic compression, and programmatic invalidation. Minimal latency in any region.
WAF with managed rules
Web Application Firewall with OWASP rules, rate limiting, and bot protection. Configured and associated with all origins.
CI/CD with Security Gate
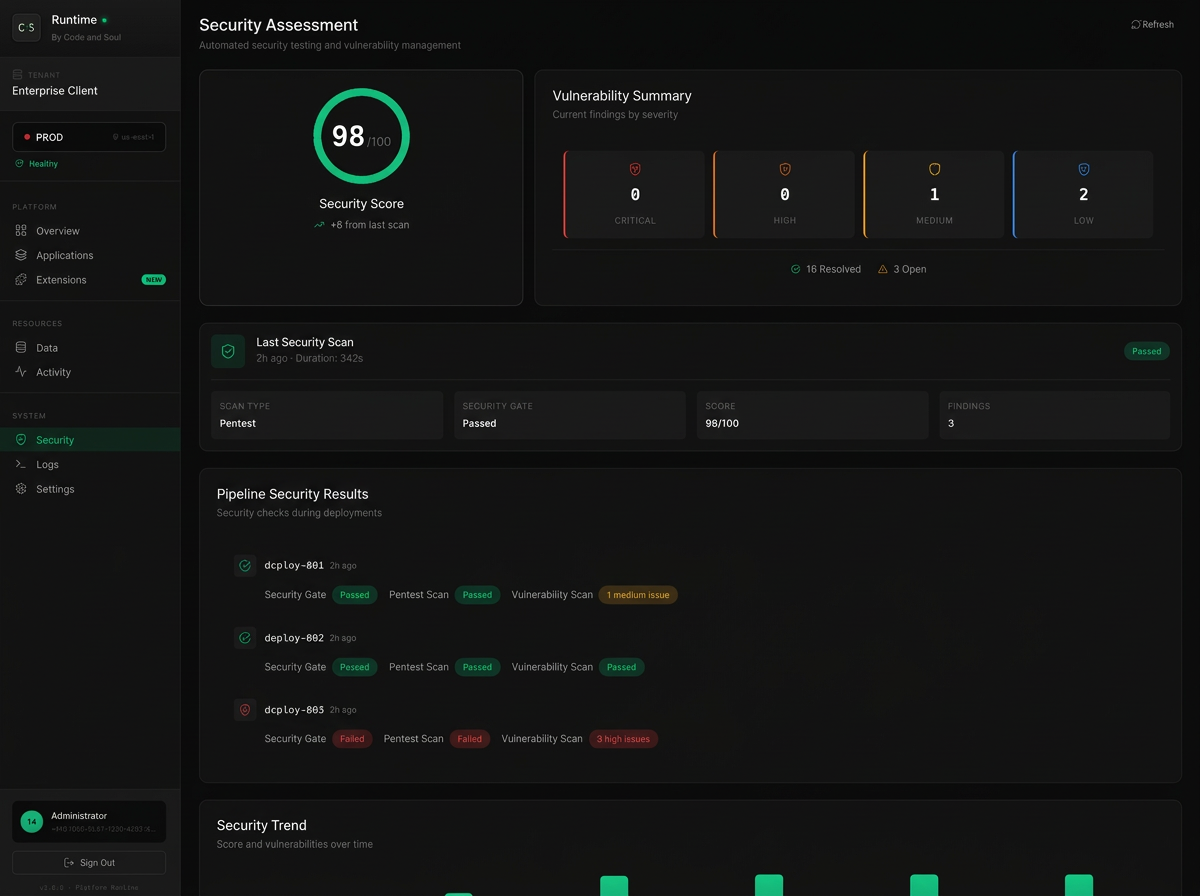
Automated pipeline with build, tests, security scanning, and deploy. No code goes to production without passing the 5 security checks.
Extension system
Modular architecture that allows adding functionality via YAML. Each extension runs isolated, with granular permissions and independent deployment.
Cost governance
Billing alerts, allocation tags, and consumption dashboards. You know exactly how much each stack component costs.
Admin dashboard
Panel for content management, configurations, and monitoring. Custom interface, integrated with the stack, no external dependencies.
No deploy without validation
Every deploy passes through 5 automated security checks before reaching production. If any check fails, the pipeline stops.
OWASP ZAP 2.17
Full DAST scanning against OWASP's 10 most critical vulnerabilities.
Nuclei 3.7
Detection of CVEs, misconfigurations, and known exposures with updated templates.
testssl.sh
SSL/TLS certificate validation, protocols, and encryption configuration.
S3 Public Access
Automated S3 bucket verification against unintentional public access.
WAF Association
Confirmation that WAF is active and correctly associated with all origins.
All checks run automatically on every deploy. Results are available in the pipeline.
Extensibility
Add functionality without touching the core
The extension system lets you create new functionality that runs inside the stack, with isolation and controlled permissions.
- →Declare functions, routes, and permissions in a YAML file
- →Each extension has independent deploy and its own rollback
- →Controlled access to core resources via secure references
name: voting
version: "1.0.1"
enabled: true
pathPrefix: /voting

functions:
  vote:
    handler: handlers/vote.handler
    memorySize: 256
    policies:
      - table: "{{core:SubmissionsTable}}"
        actions: read
Real example of a voting extension running inside the Soul Stack.
Comparison
What changes with Soul Stack
| Shared hosting | Generic PaaS | Soul Stack | |
|---|---|---|---|
| Deploy | FTP / panel | Git push | Automated CI/CD |
| Rollback | Manual | Partial | Automatic, versioned |
| CDN | Not included | Included | Global CloudFront |
| WAF | Not included | Limited | Full WAF + OWASP rules |
| SSL | Basic | Automatic | Managed ACM |
| Stack control | None | Partial | Full, in your account |
| Scalability | Limited | Automatic | Native serverless |
| Security Gate | Does not exist | Does not exist | 5 automated checks |
| Cost model | Fixed monthly | Per use + markup | Direct AWS cost |
In production
Telecom platform with national reach
Complete stack operating for one of Brazil's largest telecom carriers. Serverless infrastructure with automated security and deploys in under 15 minutes.
2100
lines of IaC
5
security checks
2
environments (staging + prod)
14
integrated AWS services
<15min
deploy time
95%
infrastructure automation
Before Code and Soul, our cloud operations were an accumulation of improvised decisions. Today we have real governance, predictable deploys, and a foundation that allows us to grow without fear. It was the most structural change we made in infrastructure in the last three years.
Caio Costa
Technology Manager·BETC Havas
No chaos. No vague promise.
Every engagement follows the same structure: understand the context, prove value fast, scale with governance.
Technical and business discovery
Clarity on what is feasible and where to start.
An operable MVP in production
Something running in the operation, not in a deck.
Scale and continuous operation
Evolution with governance, without restarting each cycle.
Ready for real infrastructure?
Talk to our engineering team. No commitment, no sales pitch. Just engineering.
Your infrastructure. Your account. Our engineering.